ARCHIVE
历史归档
按时间、分类、严重程度检索全部安全漏洞与安全信息。当前共收录 215 条记录。
智能体处理个人信息的边界如何持续有效:从Meta PrivacyLib看个人信息保护的运行机制
Meta的最新实践。 假设用户让智能体“把上周出差的费用整理好,提交报销”。为了完成这项任务,智能体需要读取邮件、提取票据、核对行程,进而调用企业的报销系统。对用户而言,自己交代的只是一件事;但在系统内部,实际展开的却是一连串个人信息处理行为。至于哪些邮件可以读取、票据是否需要发送给外部模型处理、整理出的消费记录能否存入长期记忆,往往并非在任务启动前就全部锁定,而是在任务执行过程中才逐步确定。 这给个人信息保护提出了一个直接而具体的问题…
From federal SOCs to Talos: Ryan Fetterman on practical security research
What does it mean to be "blue collar" for the blue team? Ryan Fetterman discusses the realities of detection engineering, and shares his philosophy on building a career in security without burning out.
Apple Patches for October 2026, (Mon, Oct 26th)
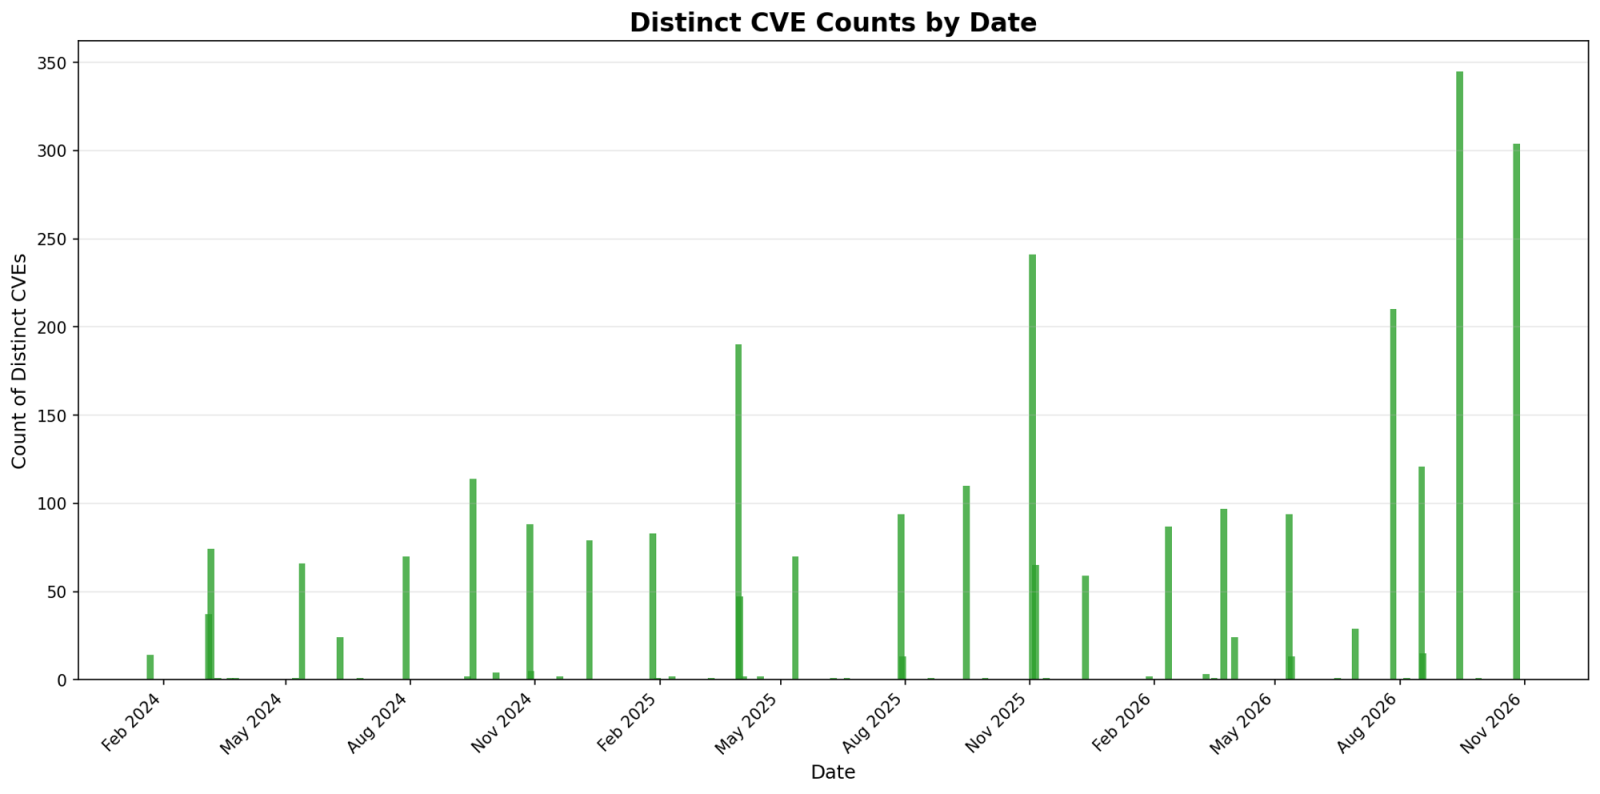
Apple today released patches for 304 vulnerabilties. This number is still in line with prior Apple updates, and comes just about a month after the last apple update.
CVE-2026-48356:Adobe Commerce and Magento Unrestricted Upload of File with Dangerous Type Vulnerability
Adobe Commerce and Magento contain an unrestricted upload of file with dangerous type vulnerability that could result in arbitrary code execution in the context of the current user, potentially gaining elevated access or…
CVE-2026-111497:Google Brotli Unchecked Return Value Vulnerability
Google Brotli contains an unchecked return value vulnerability that allows a remote unauthenticated attacker to corrupt adjacent decoder state memory, disclose sensitive memory contents, cause a denial of service, or pot…
Looking for a Language [Guest Diary], (Wed, Oct 21st)
[This is a Guest Diary by Jeffray Spence, an ISC intern as part of the SANS.edu BACS program]
YARA-X 1.22.0 Release, (Sun, Oct 25th)
YARA-X's 1.22.0 release brings 11 improvements and 9 bugfixes.
CVE-2026-109619:PHP Stale Internal Request-State Vulnerability
PHP contains a stale internal request-state vulnerability that allows for unauthenticated remote code execution.
CVE-2026-109618:PHP Memory Corruption Vulnerability
PHP contains an out-of-memory corruption vulnerability that allows for unauthenticated remote code execution.
CVE-2025-41242 代码审计与复现:利用“幽灵比特”突破 Spring 路径穿越防线
CVE-2025-41242是Spring Framework高危路径穿越漏洞,利用Java字符高位截断(幽灵比特)特性,构造特殊Unicode字符生成畸形 %uXXXX 编码,实现跨组件解析不一致绕过,突破Spring路径黑名单校验,在Jetty底层还原出目录穿越符号读取敏感文件。本文从代码审计、漏洞复现到补丁验证完整复盘该漏洞,分析利用链并给出安全防御方案。
基于 nRF Sniffer 的 BLE 智能灯泡协议逆向与重放攻击
本文详细记录了对某智能灯泡的低功耗蓝牙(BLE)安全测试全过程。文章从 Wireshark 与 nRF52832 抓包环境的搭建切入,直击物联网设备通信痛点,演示了如何捕获设备指令、逆向分析 GATT 读写 Payload,并成功利用 nRF Connect 实施重放攻击接管设备。文末针对实测漏洞,提出了引入随机数、挑战-应答机制及链路层加密等安全防护建议。
基于小语言模型的 RAG 流水线上下文感知提示注入检测:nokast-secureRAG
作者:Abhishek Rai 原文链接:https://arxiv.org/html/2610.28364v1 摘要 本地检索增强生成(Retrieval-Augmented Generation, RAG)系统让强大的智能助手能够在私有数据上运行,但也继承了一类日益增长的安全风险——尤其是间接提示注入(Indirect Prompt Injection, IPI)与检索投毒,即隐藏在检索内容中...
讲解一下这次PHP核弹级别漏洞的原理
作者:Laruence 原文链接:https://mp.weixin.qq.com/s/bB2EqImUlslJGCs7melQGw 这几天PHP圈很热闹,AI发现了一个核弹级别,隐藏了十几年的PHP的RCE漏洞,连日本首相都发X提醒大家注意。哈哈哈 本来昨天就想写一个分析的,不过考虑到可能被攻击者利用,就等到Patch出来以后,今天再发吧,本文以已经公开的攻击脚本POC为例,来解释,具体链接我就...
CVE-2026-6307:漏掉一次签名比较,Wasm 返回类型错乱
TurboFan 把两条返回类型不同的 JS→Wasm 调用点内联进同一个函数时,帧状态判等函数漏掉了 Wasm 签名的比较,两份帧状态被判成同一份;一次惰性反优化之后,返回值按错误的类型物化——对象地址被读成整数,整数被当成对象指针。
深度复现 CVE-2026-23918:Apache HTTP/2 拒绝服务与 RCE 利用链探究
CVE-2026-23918 是 **Apache HTTP Server 2.4.66** 版本中 `mod_http2` 模块存在的高危内存破坏漏洞。