威胁情报
NIK C2: The new AI-enabled command-and-control framework
Cisco Talos observed a new AI-integrated command-and-control (C2) framework in the wild called “NIK C2.”
ARCHIVE
按时间、分类、严重程度检索全部安全漏洞与安全信息。当前共收录 261 条记录。
Cisco Talos observed a new AI-integrated command-and-control (C2) framework in the wild called “NIK C2.”
Telegram安卓端存在高危漏洞,用户仅需接听语音通话就可能被攻击者执行任意代码,请尽快升级至12.10.4及以上版本。
An attacker tried to exploit a critical GitLab vulnerability on the Alpine Linux project's own GitLab server a week after GitLab released a fix, Alpine Linux said on 28 October. The flaw, CVE-2026-97229 (CVSS score: 10.0…
Hackers exploited a critical Cisco Catalyst SD-WAN flaw, fixed in February, to plant custom malware inside the systems that control an organization's SD-WAN network. The malware, called KeyDrift, is designed to copy the…
Claude成功编写出Linux内核高危漏洞利用程序,远程攻击者无需交互即可获取root权限,漏洞已修复,请及时更新补丁。
量子计算机可破解现有加密体系,存在“先收集后解密”风险,NIST发布后量子密码迁移指南,明确迁移路径与时间节点,指导机构抗量子升级。
未发布版Claude可构建多平台高危漏洞利用链,一键攻破Chrome、零点击获取Linux Root权限、绕过安卓锁屏,漏洞已修复请尽快打补丁。
AI 网关三产品同陷密钥危机:Kong 让请求头决定密钥去向;APISIX漏声明加密字段,etcd 落盘明文;Higress 客户端可控,配套 ai-gateway-audit.py 一键自查。
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a security flaw impacting Broadcom VMware ESX to its Known Exploited Vulnerabilities (KEV) catalog, after CrowdStrike revealed that it h…
Building your malware analysis lab is a key point before playing with malware. Today, thanks to virtualization, it's convenient to play with snapshots in your lab. Start a new investigation from a clea…
Palo Alto Networks on Wednesday warned that threat actors are exploiting the recently patched PHP2Shell vulnerabilities against publicly-accessible management interfaces. "Active exploitation has been observed targeting…
国家背景黑客利用思科SD-WAN无认证满分0Day漏洞植入KeyDrift,窃取加密密钥入侵航天国防等机构,需立即打补丁排查。
复现环境:Ubuntu 24.04.4 LTS,Python 3.12.3,venv 隔离。授权服务器和 MCP 资源服务器都跑在这一台机器上,监听 127.0.0.1,端口 9000 和 8001;代码取自官方示例 examples/servers/simple-auth(tag v2.3.0)。对照组另外起了两个实例:一个跑 2.0.0 的授权服务器(端口 9100),一个给授权服务器套上 S
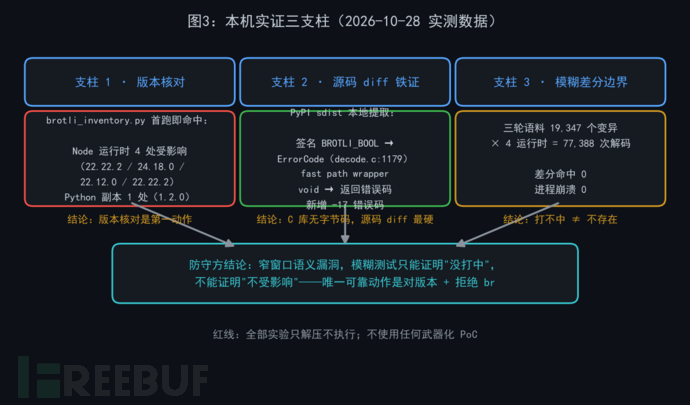
Brotli 越界写让一个压缩包双向打穿 Node.js。本文用版本核对、源码 diff、模糊差分三支柱完成本机实证,首跑命中 5 处受影响副本,附核查工具与修复矩阵。
2025年爆出的某电子签署平台验签功能 /api/pdfverifier 漏洞还是比较经典的。本身是 Jar 包启动的Web服务,验签漏洞是 zip 文件上传然后ZipSlip 漏洞,在这个场景下进行RCE。本篇文章主要记录下签署平台在该ZipSlip漏洞下的RCE方式。
01前言在日常的应急处理过程中,要结合系统各种日志来排查该告警是真实告警还是误报。本篇文章就来看看linux中常见的一些日志,以及其作用,目的是为了在应急响应时可以快速的找到排查目标02linux中常
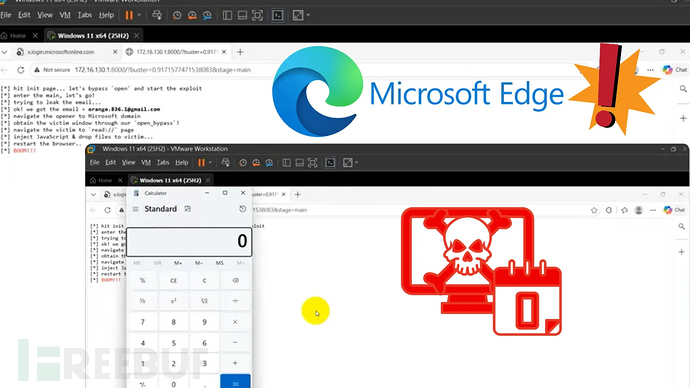
研究人员披露微软Edge存在串联5个漏洞的零点击利用链,无需内存破坏、无需额外点击即可突破沙箱在Windows执行代码,用户需尽快安装安全更新。